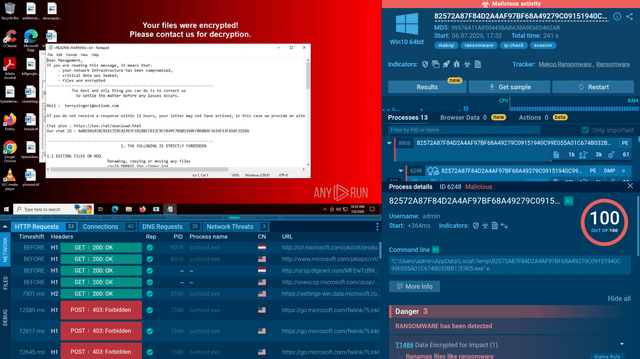
What is Makop?
Makop is a Phobos-derived Ransomware-as-a-Service model that primarily targets exposed and vulnerable RDP endpoints. Human operators manually navigate compromised networks to escalate privileges, map assets, disable defenses, and deploy the ransomware payload.
Key Features
- Background and History: First seen around 2020, Makop is a Ransomware-as-a-Service model derived from the Phobos ransomware family, with ransom demands averaging around $15,000.
- Hands-On Attackers: Campaigns are human-operated, with attackers manually scouting targets, stealing logins, escalating privileges, and disabling antivirus before deploying the payload.
- Multi-Stage Loaders: Operators use third-party tools like GuLoader to deliver secondary malware, making initial perimeter detection harder.
- Defense Evasion via BYOVD: Attackers use Bring Your Own Vulnerable Driver (BYOVD) tactics, loading legitimately signed but vulnerable drivers to gain kernel access and terminate EDR agents.
See the full sandbox analysis and learn how to detect and mitigate this threat: https://any.run/malware-trends/makop/
https://i.redd.it/k6a8sehudqmh1.png
Source: r/ANYRUN · by /u/ANYRUN-team