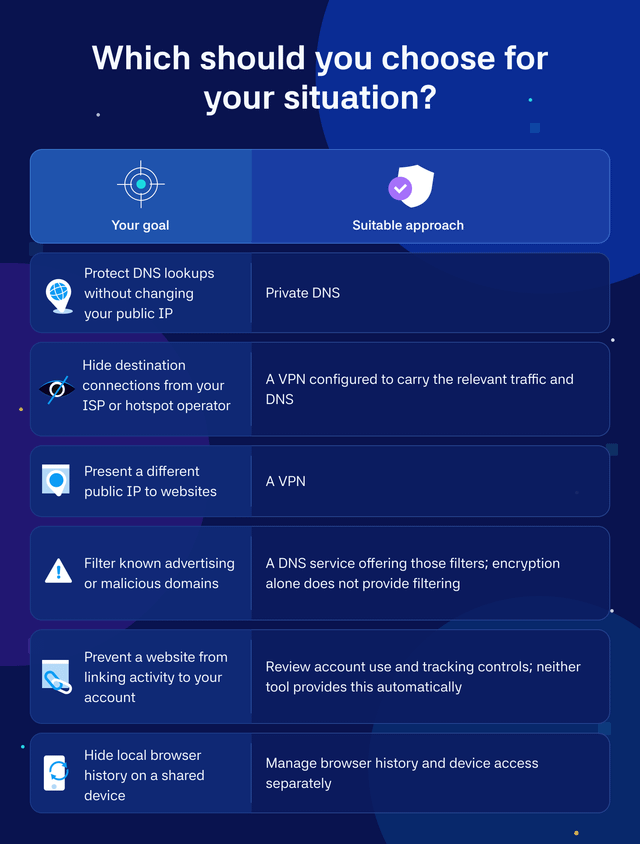
Private DNS can encrypt your DNS lookups, but your ISP can still see the destination IP addresses of your direct connections.
Those addresses don’t always identify a specific website: many domains share infrastructure. However, they can provide clues. A hostname exposed during the TLS handshake can reveal more, unless protections such as ECH apply.
Here’s how the layers differ:
- Encrypted DNS protects lookups between your device and the resolver. The resolver still receives those queries.
- HTTPS protects page contents, searches and messages in transit.
- A correctly configured full-tunnel VPN conceals the destination connections carried through it from your ISP. The ISP still sees the VPN endpoint, timing and traffic volume.
- Websites can still recognise your logged-in account, regardless of either setting.
There’s also a detail that can make DNS tests confusing: seeing a third-party resolver doesn’t automatically prove a leak. Its connection may still travel through the VPN tunnel. You need to compare the result with your intended configuration.
We’ve published a breakdown at hide.me covering visibility, browser Secure DNS settings and practical checks:
Private DNS vs VPN
Do you use your VPN’s default DNS, a custom resolver, or your browser’s Secure DNS?
https://i.redd.it/0lc7nn76a6zh1.png
Source: r/hidemeVPN · by /u/hidemevpn