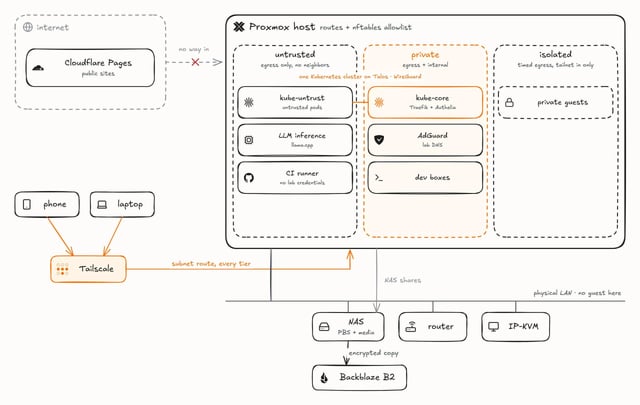
one proxmox host (a thinkcentre m70s) and a synology NAS in a 16U rack, just for me. it's where i actually work: my laptop is mostly a terminal into two dev boxes in the rack, where my coding agents run too, next to stuff i use daily like jellyfin, paperless, my notes, bookmarks and a local LLM. tried to draw the whole thing on one page.
the host routes everything, and guests sit on bridges grouped into three tiers: untrusted (CI runner, LLM box, the kube node for stuff i don't vouch for), private (the main kube node, adguard, my dev boxes) and isolated. the idea is to split the lab by trust like a cloud VPC, so anything handling traffic i don't vouch for (downloads, CI running pull requests) lands on the untrusted node, which holds no keys and can't reach its neighbors.
the firewall is a single nftables allowlist on the host. kubernetes is two talos VMs, one per tier. i reach it all through a tailscale subnet route on the host, no port forwarding. backups go to PBS on the NAS, then an encrypted copy to B2.
i know it's one box, so no HA, and if the host dies everything goes with it. that's a trade-off i accepted for a home setup, my goal is to lose at most a day of data, not to never go down.
what would you do differently?
https://i.redd.it/7cwrlgj4c0xh1.jpeg
Source: r/homelab · by /u/OddWaltz6121