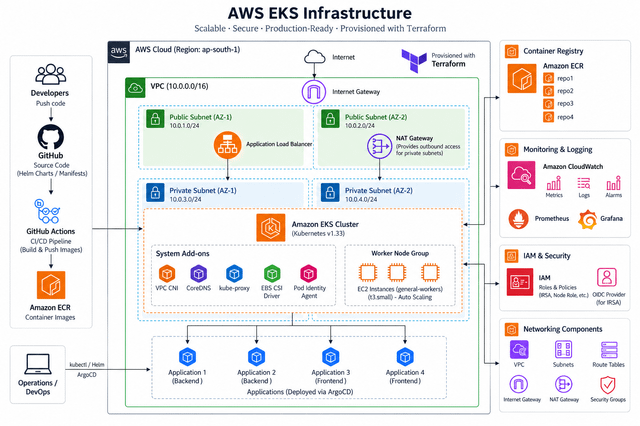
I got tired of creating the same AWS infrastructure for every Kubernetes project, so I built a reusable Terraform template that provisions an entire Amazon EKS environment in about 5–10 minutes.
What it creates
- Amazon EKS cluster
- Custom VPC with public/private subnets across multiple AZs
- Internet Gateway + NAT Gateway
- Route tables, NACLs, and Security Groups
- Managed Node Groups with autoscaling
- IAM Roles + IRSA (OIDC)
- Amazon EBS CSI Driver
- CloudWatch log groups
- Amazon ECR repositories for microservices
The idea was simple: change a few values in terraform.tfvars and reuse the same infrastructure for any project.
Example:
project_name = "revenuepilot" cluster_name = "revenuepilot-eks" aws_region = "ap-south-1" Then:
terraform init terraform apply One challenge I learned a lot from
The EBS CSI Driver initially couldn't create volumes because of IAM permission errors.
I ended up implementing IRSA (IAM Roles for Service Accounts) with the cluster's OIDC provider instead of relying on node IAM permissions. After configuring the trust relationship in Terraform, PVCs started provisioning EBS volumes correctly.
That debugging session taught me a lot about how Kubernetes identities map to AWS IAM.
Project structure
networkingmoduleiammoduleeksmoduleecrmodule
Everything is parameterized and ready to plug into a GitOps workflow (Argo CD / Helm / GitHub Actions).
I'm a final-year CS student learning DevOps, so I'd genuinely appreciate feedback from people who manage EKS in production
https://i.redd.it/hcmem3aq2tph1.png
Source: r/u/Fast_Caregiver_4240 · by /u/Fast_Caregiver_4240