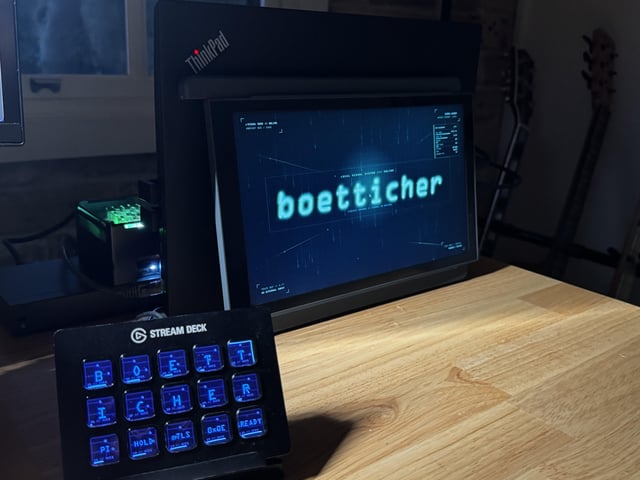
Posted about a week ago about how I am dipping my toes into the homelab world with an old Lenovo t580 laptop and a dream. Think have escalated a little bit so I now have;
- Lenovo t580 (Core i5 / 32GB RAM / 256GB SSD)
- 1TB external SSD (scavenged)
- Raspberry Pi 4 with a 2TB SSD (old project)
- Portable 12" monitor connected to the Pi via HDMI for Kiosk duty
- StreamDeck
- TP-Link 8 port Managed POE switch
On the laptop I'm running;
- Proxmox
- Debian firewall VM – nftables, DHCP, and DDNS
- Blocky/Chrony LXC – DNS/NTP
- systemd logs LXC – log shipping and querying
- Pulse LXC – Monitoring
- SOPS + systemd – secrets management
- Ansible – deployments and host management
- I've built a few modules which all run as unprivileged LXCs and working on more;
- Tailnet LXC – pushes 10.10/16 routes into tailnet for remote access
- AirVPN LXC – allows routing traffic out from a homelab server via AirVPN (in progress)
- StreamDeck LXC – polls Proxmox and displays the state of my various hosts (in progress)
- Octoprint LXC – allows remote management of my 3D printer (in progress)
- LiteLLM LXC – LLM router to give secure access to vendor-hosted models (currently OpenRouter-only)
- AIOps LXC – HolmesGPT instance which can use Pulse and systemd logs to investigate issues in the cluster using AI models via LiteLLM (planned)
- Gatus LXC – simple status page (planned)
The network is a little bit overengineered, which is half the fun;
Managed Switch
- (VLAN1) Home internet uplink (192.168.x.x/22)
- (VLAN1) Home Wifi Mesh Access Point
- (VLAN1) Lab WAN interface (built-in NIC)
- (TRUNK) LAB LAN interface (USB NIC)
- (VLAN30) LAB TRUSTED access port – personal laptop
- (VLAN40) LAB SANDBOX access port – work laptop and other untrusted devices
- (VLAN20) LAB SERVERS access port – Kiosk Raspberry Pi 4
- SPARE
Internal bridge (vmbr01) – 6 Proxmox vNICs attached to the firewall VM
- (VLAN5) LAB TRANSIT network – Tailnet and AIrVPN routers
- (VLAN10) LAB INFRA network – DNS, NTP, Pulse, Logging
- (VLAN20) LAB SERVERS network – Kiosk Pi (for now)
- (VLAN30) LAB TRUSTED network – full access to all lab networks
- (VLAN40) LAB SANDBOX network – just internet access
- (VLAN99) LAB MGMT network – access to Proxmox console
Future Plans
- Jellyfin server (when I get more storage)
- *arr Stack (torrenting via the AirVPN router)
- Home Assistant
- Cloud Storage
- Private Email (inbound-only)
Automation
I started out with OpenTofu and Ansible, but I have actually moved to a homemade Go-based orchestrator. I don't want to advertise it for a couple of reasons; 1) it's entirely vibe-coded, and 2) it's not very good yet! At some point I might open-source it. Basically it starts from a clean Proxmox install and builds pretty much everything. It's very opinionated and it basically builds the lab I want, but I've added some fun QoL features like network testing, module management (so I can turn on AirVPN or Gatus using CLI commands), and support for an external firewall instead of the built-in Debian one.
It's been fun…I could definitely never have built it myself.
https://i.redd.it/jpf87k4rpumh1.jpeg
Source: r/homelab · by /u/Alexis_Denken