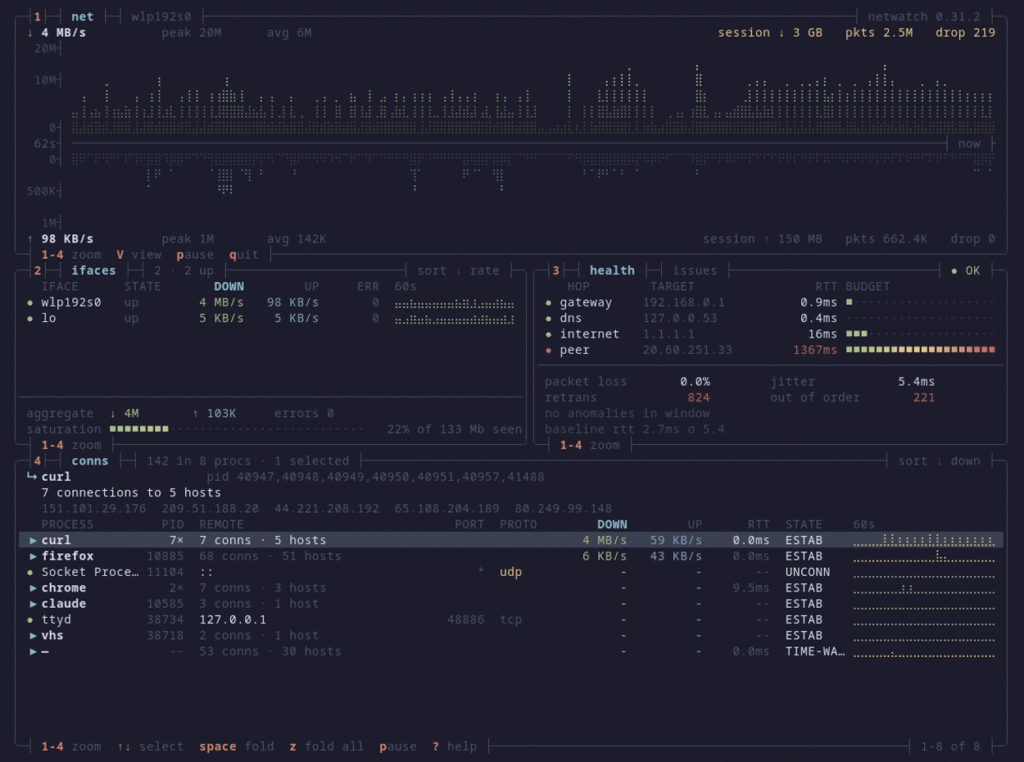
Ten tabs over your network, all one keypress apart:
– Every socket with the process behind it, PID, TCP state, GeoIP, RTT and retransmits. Attribution comes from platform socket polling, PKTAP on macOS, and an optional eBPF kprobe on Linux.
– Live packet decode with display filters, stream tracking, JA4 fingerprinting and PCAP export.
– TLS 1.3 and 1.2 decryption for sessions you hold the keys to. Point a client's SSLKEYLOGFILE at NetWatch and the plaintext decodes in the Packets tab, same mechanism as Wireshark.
– A diagnostic engine that learns per-metric baselines, opens an issue when one breaks, ranks the causes by the checks that separated them, and closes the issue only once the fix has held. No model involved.
– Egress drift. It learns which hosts, autonomous systems and ports each process reaches, you promote that to a rule, and the next new destination shows up flagged. Observes only, never blocks.
– Background detection for C2 beaconing, port scans and DNS tunnelling. A critical alert freezes the flight recorder so the bundle exists before you go looking.
– Throughput, interfaces, protocol breakdown, traceroute topology, per-process bandwidth, and a timeline of connections by TCP state.
– Three layouts off one capture. V cycles them live: full ten tabs, –lite for 80×24, –view dense for four borderless boxes with braille throughput graphs.
macOS, Linux and Windows. One binary, no config. The Linux build is static with libpcap bundled in.
brew install netwatch
cargo install netwatch-tui
https://i.redd.it/1e9on62h2dqh1.gif
Source: r/selfhosted · by /u/Potential-Access-595