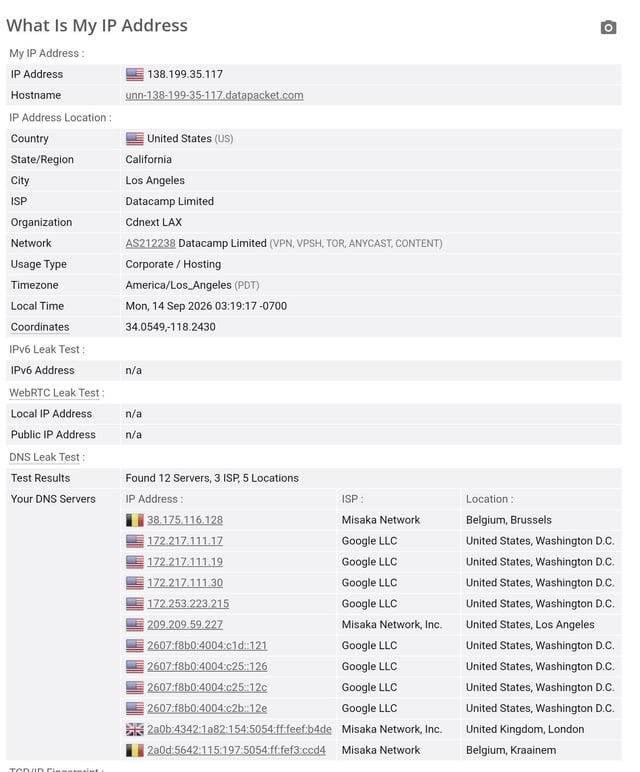
Issue: Every single DNS leak test I've done, reveals DNS leaks to Google server when using accurately configured NextDNS or ControlD endpoint resolvers configured in RethinkDNS with either DoT or DoH.
There is no leak when I use any of the "built in" resolvers. So something IS leaking when using custom endpoint resolvers. How to fix this?
This is my comprehensive setup for troubleshooting purposes:
- RethinkDNS 0.5.6 (fdroid)
- NextDNS resolver configured in RethinkDNS: Other DNS – DoT – tls://xxx.dns.nextdns.io
- Proxy configured in RethinkDNS: Import – .conf file (I've tried Surfshark, Mull and and Proton VPNs). ONLY ONE VPN PROXY HAS BEEN ACTIVE AT ANY GIVEN TIME.
Options configured (only will mention options toggled ON, if not mentioned means all other toggled OFF):
- DNS
- Show website icon in DNS logs
- DNS booster
- Prevent DNS leaks
-
Block DNS from Unknown source
-
Proxy
-
Advanced – Lockdown
-
Android system
-
Private DNS OFF (mentioning it specifically)
-
VPN – Rethink – Always-on VPN Block connections without VPN
-
RethinkDNS Firewall – Universal firewall rules
-
Block all apps when device is locked
-
Block when DNS is bypassed
-
Block newly installed apps by default
-
Block port 80 (insecure HTTP) traffic
Edit : important to note, the DNS does not leak if I'm using any of the mentioned VPN'd native android app.
https://i.redd.it/w3nxk8dt1hph1.jpeg
Source: r/rethinkdns · by /u/niclaw13