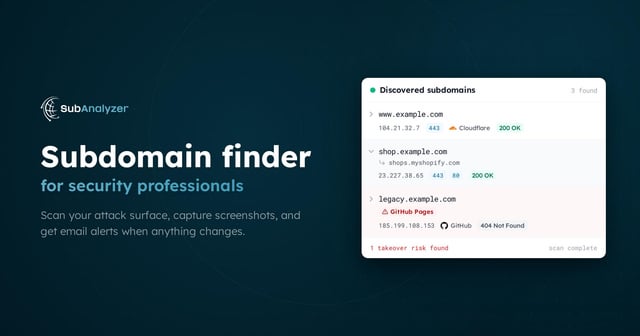
We’re building SubAnalyzer, and would like feedback on its monitoring service from people who already run their own recon pipelines.
It reports new and removed subdomains, DNS and service changes, and potential takeover risks. You can choose which changes trigger alerts, with updates grouped into an email digest.
One design detail: manual scans stay separate from monitoring alerts, and changes are compared with the last reported state rather than simply the last scan.
We’d like to hear how others decide which changes deserve attention. Do you investigate every new hostname, focus on newly exposed services, or prioritise changes involving particular providers?
We also have an API coming. Which would be more useful in your setup: pulling change data into existing tools, or controlling scans and monitoring programmatically? Those are questions about what to prioritise, not announced API capabilities.
Disclosure: we operate the service. Monitoring is paid, and there’s a free scanning tier.
Source: r/cybersecurity · by /u/TallSession9532