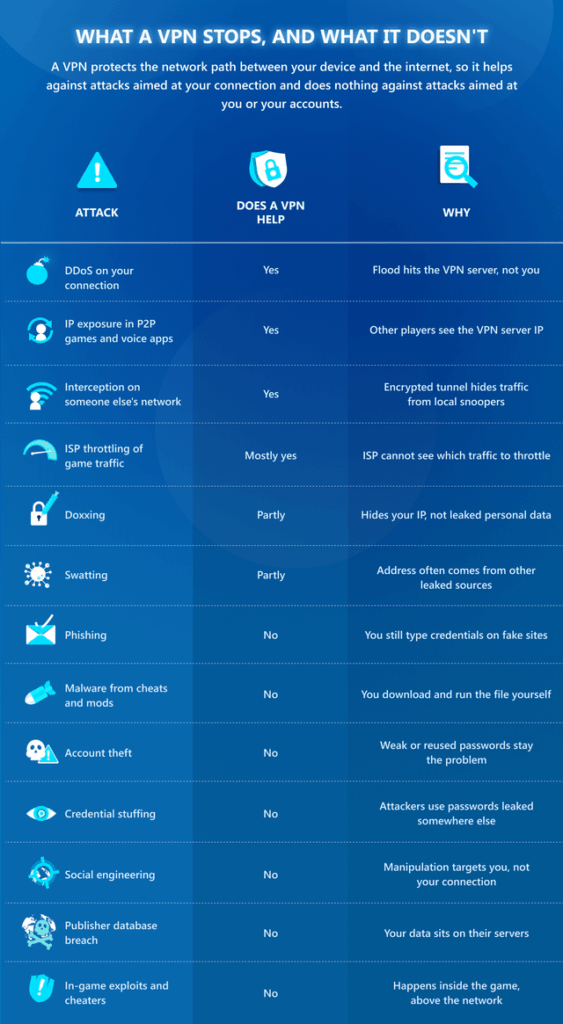
We run this sub, so treat the source accordingly. But the useful half of this is the part that argues against us, so here it is first.
Where a VPN does nothing:
Account theft and credential stuffing. Leaked credentials get replayed from the attacker's machine. Your traffic was never in that flow.
Session token theft. This is the one more people should know about. You log in normally, the platform issues a session token, the token sits in your browser. Infostealer malware reads it. The attacker replays your already completed login without a password and without triggering 2FA. Nothing about tunneling your traffic touches this.
Malware from cheats, mods and cracked games. Flare analysed 53,896 infostealer-infected devices in late 2025 and found 41.47% of infections came from a gaming-related file. The largest category in the set. Unofficial mods and cheats for GTA, Roblox, Valorant, Counter-Strike and Fortnite were the top five sources. 17.65% of all infections involved a cracked version of the software the user actually wanted.
The reason it works so well is procedural, not technical. These downloads usually come with instructions to disable antivirus first because the "tool" gets flagged. The user removes their strongest on-device protection immediately before executing an unknown binary.
Phishing. Fake giveaway and trade pages, fake tournament invites, a DM from a friend's compromised Discord. Some fakes now render a convincing fake browser window with a fake address bar inside the page. If you enter credentials voluntarily, a VPN is irrelevant.
In-game cheating. Happens in the client or against publisher servers. Anti-cheat and reporting are the only levers.
Fair disclosure: we ship DNS-level filtering that blocks known malicious domains, and other providers do similar. It helps, but it is an add-on rather than the VPN doing its job, and it only covers domains already identified. Phishing infrastructure is deliberately short-lived to stay ahead of exactly that.
Where it does help:
DDoS, with two conditions. It has to already be running when the attack starts, and the attacker must not already hold your real IP. If your address was captured before you connected, that address stays targetable. A VPN protects what you present from now on. It cannot pull back something already logged.
IP exposure in games that use direct connections. Fighting games commonly do this for latency reasons, Street Fighter 6 among them. GTA Online public sessions still use a peer-to-peer mesh with players exchanging UDP directly. In June 2026, players of one Steam title reported its public lobbies used direct unencrypted P2P and exposed every participant's address.
Titles on dedicated infrastructure are a different situation entirely. Steam Datagram Relay forwards encrypted traffic through Valve-operated relays rather than letting endpoints connect directly, and Valve has said reducing DDoS was part of the reason.
A few things worth knowing regardless:
Restarting your router may or may not get you a new IP. Dynamic does not mean different. Check afterwards with a lookup tool instead of assuming.
Router-level filtering will not save you from a real flood. By the time the traffic hits your router it has already eaten your bandwidth. Your ISP is the escalation path.
Consoles have no VPN client. Router configuration or sharing a connection from a PC are the only two routes.
If you do one thing from this post, make it signing out of all active sessions on your gaming and email accounts. That is what kills stolen tokens, and it is the step people skip after a malware scare.
Full write-up with the doxxing and swatting section and the ISP throttling detail: https://hide.me/en/blog/the-most-common-attacks-on-gamers/
Question for the sub: for those of you who have actually been hit, was it a DDoS or was it an account takeover? I suspect the ratio in here looks nothing like what people expect going in.
https://i.redd.it/vuz330mtzgnh1.png
Source: r/hidemeVPN · by /u/hidemevpn