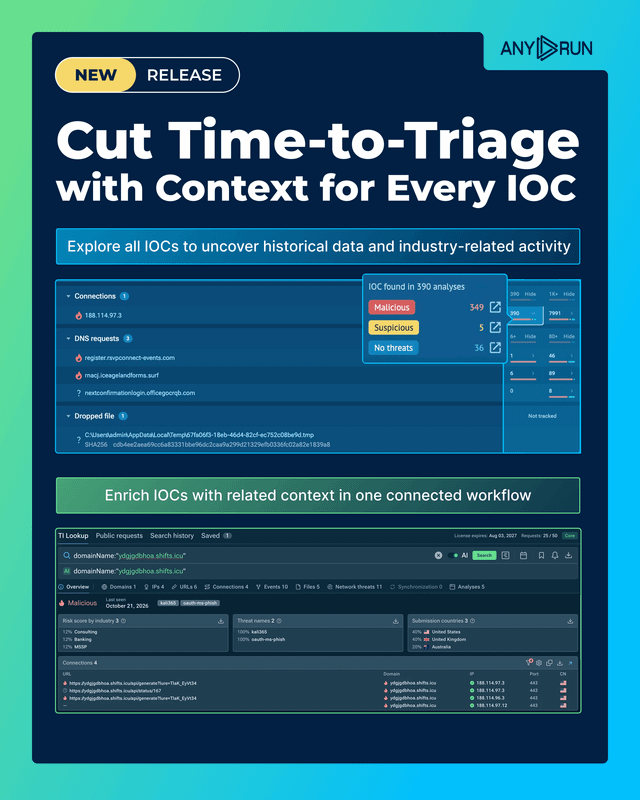
SOC & MSSP teams used to manually rebuild the picture around every suspicious IOC. With this new ANYRUN update, you can see related team analyses, historical context, and industry-related activity for every IOC and uncover related infrastructure in one connected workflow.
𝗜𝘁’𝘀 𝗿𝗲𝗮𝗹𝗹𝘆 𝘀𝗶𝗺𝗽𝗹𝗲: review the context around each indicator in the Sandbox, then pivot to TI Lookup in one click to uncover additional threat activity and give Tier 1 evidence to justify escalation.
See the workflow in action and try it yourself: https://app.any.run/tasks/390e708f-2dce-4141-a990-2cb4da4977be/
Connected context brings a whole new level of speed and clarity to triage: faster decisions, fewer uncertainty-driven escalations, more focused use of Tier 2 expertise, better knowledge reuse across shifts, and stronger visibility into industry-relevant activity.
🎉 𝗧𝗵𝗲 𝘁𝗿𝗶𝗮𝗴𝗲 𝗯𝗼𝗼𝘀𝘁 𝘆𝗼𝘂’𝘃𝗲 𝗯𝗲𝗲𝗻 𝘄𝗮𝗶𝘁𝗶𝗻𝗴 𝗳𝗼𝗿 𝗶𝘀 𝗵𝗲𝗿𝗲. Explore Related Threat Context in your security workflows: https://any.run/cybersecurity-blog/related-threat-context-release/
https://i.redd.it/gphmspi2w0xh1.png
Source: r/ANYRUN · by /u/ANYRUN-team