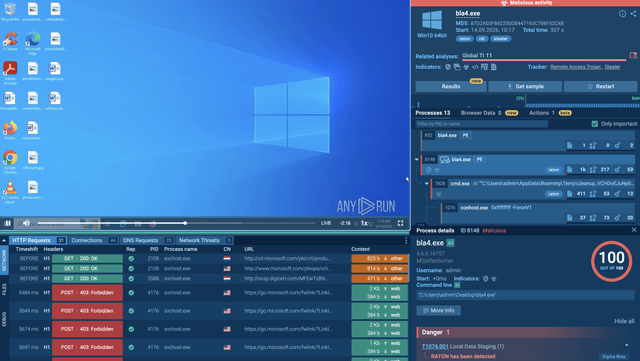
What is RatonRAT?
RatonRAT is a .NET-based Remote Access Trojan targeting Windows systems. It supports credential theft, screen capture, system discovery, persistence, and C2 communication.
Key Features
- Credential & Data Theft: Steals credentials and collects system and hardware information.
- Persistence: Uses scheduled tasks and Active Setup to maintain execution after user logon.
- Defense Evasion: Bypasses PowerShell ExecutionPolicy and adds its process to Microsoft Defender exclusions.
- System & VM Discovery: Checks running processes, privileges, BIOS and disk information, plus VirtualBox and VMware environments.
- C2 Communication: Connects to a configured C2 server to receive further instructions.
- Configurable .NET Malware: Uses a configurable .NET architecture and Costura/Fody to bundle components.
How to detect and reduce exposure: https://any.run/malware-trends/raton/
https://i.redd.it/h51ni0eg92rh1.png
Source: r/ANYRUN · by /u/ANYRUN-team