tl;dr: Seeking free advice or a paid mentor/advisor (ideal for Bay Area side income) to resolve a security setup issue and guide implementation.
Hi, I’m Redacted, studying for CompTIA+. I’m conceptually intermediate–advanced but practically a beginner. My mistake: buying and storing equipment I wasn’t ready for; missing components left most items boxed and a few unboxed. I shelved the project until I could prepare better.
Thanks to volunteers; I’m open to hiring 1–2 credentialed experts for private mentorship (comments only for now due to many sub rules about DMs/scams) until resolved. This is my last option before discarding everything—I’d rather pay part of the cost for help.
1) The critical error:
I live in a 1970s garage with gaps in the wooden door, two mesh-covered vents that have direct access to a nearly 4ft tall bedroom sized crawl(more like crouch) space that is easily accessible from the front of the house via a crosshatched wood barrier WITH a little door section unlocked but for a tiny exterior latch, and an easily compromised 1 screw electronic keypad outdoor and old opener indoor on the garage side. Due to financial limits and housemates blocking internet upgrades, I left an open box containing a Ubiquiti UDM SE, 2–3 U6 Pro APs, cameras, coax, and Ethernet cables—intended for a full system. Earlier, a housemate misused a Netgear Nighthawk 7, misunderstanding its limitations.
2) What physical signs suggest exploitation or poisoning of multiple devices? What evidence exists, and what failed fixes have I tried?
I noticed overnight DoS attacks in Nighthawk logs and unexplained terabyte-level Wi-Fi usage. After hardening security, I wrote recovery keys in a notebook; later, the codes were altered with pen marks (e.g., L→H, 3→8), making them unusable. My cohabitants doubt physical access, but I live in a garage with outdated mechanisms and frequent vacancies. Two vents lead to a 4-ft crawlspace under the deck, adjacent to the only internet point: an unlocked outdoor cabinet labeled “Electric” containing the Xfinity coax. The coax was supposed to run through a visible switch into a network cabinet near a sliding glass door, right above the crawlspace. After someone replaced the Nighthawk 7 with a simpler Comcast modem for Netflix, the setup remained exposed. They do nothing else. Note: all other house members have a 4th-gen Nest Thermostat and a front door cam (with physical and app disable switches 🤦🏽♂️) that triggers randomly—especially during expensive deliveries or network changes.
After returning from a trip, I found fresh, damp spackle over drilled holes and in-wall wiring in my garage—clearly new patches. A UDM-SE unit appears disconnected and missing its door; its front panel is mismatched and heavier, suggesting possible substitution. Given physical access risks and potential in-wall hardware, how can I actively test for hidden devices—especially if my “Home WiFi” is a restricted VLAN with DNS spoofing or outbound limits? I suspect possible network injection via FTP, file sharing, or compromised Apple/iCloud credentials amid spoofed handshakes and APs.
I can’t list all attack points or confirm them before construction. After my initial gear, the outdoor coax setup changed: ISP gray box → 1:1 grounded connector became a thicker, foam-covered dual-cable run through the cabinet’s crawlspace hole (protected by peelable mesh) and back up to the closet. Two coax cables emerge—one to the grounded connector and Xfinity XB8-T gateway (app-only control). In the crawlspace, a second cable passes through a hidden vent behind a fridge; IR/wall detectors show it entering an unprofessional hole in the garage ceiling near two unused holes. My tall, narrow condo likely routes a second coax from the vent through the garage ceiling—either toward the breaker (near spackling) or into a space for UniFi gear (AP, switch, UDM-SE). I could use concealable options like the paintable UniFi Wall (10 Gbps, thin cables) screwed into wall gaps—especially behind kitchen cabinets or the dishwasher—or UniFi’s crown-molding wire covers with L-joints. This would create a mesh network controlling all Wi-Fi devices; since most activity requires Wi-Fi, our searches and equipment purchases are constrained.
4) What I’ve tried and am doing to assess the issue’s scale:
I need to determine whether this is simple packet/data theft targeting me and my complex—mostly older residents sharing coax access—or a broader compromise of devices on my Xfinity Wi-Fi. I’ve added a GL.iNet Mudi 7 (USB tethering via 5G SIM/eSIM, cellular Wi-Fi, or wired 2.5 GbE; I reject repeater mode) and plan to use other GL.iNet and ASUS gear for an independent setup. I suspect tampered hardware (e.g., a heavy charger with a Quectel chip). Should I use HackRF, Splunk, Nmap, or a Panda Wireless adapter to detect rogue APs, or are there better diagnostic options? I’m weighing options from an ESP32 with Marauder on SIM and Kingston encryption to pre-secured Linux devices like the Purism Librem 16. I want to replace visible UniFi gear with a custom Dream Router running UniFi OS or OpenWRT, plus a domain (and possibly a server—seeking a paid build partner). I’m considering NextDNS/OpenDNS/Cloudflare with a VPN (OpenVPN like Nord/Express or WireGuard like Mullvad/IVPN).
How do I mitigate this threat and who can help? I need a secure 2U–6U UniFi cabinet design—possibly inside my safe—with a lock and metal frame. I want a simple, self-contained system using UniFi OS, Protect, Endpoint, and ID verification; clarify overlaps (e.g., AI Keystones, Cloud Key Plus). Provide initial setup steps via web portal or apps on a dedicated device, guidance on finding a clean or hidden network for a UniFi iOS account, and instruction on analyzing iOS data (IPS, endpoint detection) with proper gear. Including this would teach setup of 4–5 VLANs plus a management network for one mostly air-gapped device backed up continuously to a 1–2 TB Kingston IronKey with isolated hardware and OS. (Note: I expect this may be removed for length and off-topic content; do not DM.)
Seeking a paid cybersecurity consultant (remote advice to full build/mentorship) at a fixed rate based on scope and time. I have wiped MacBooks, plan to get an iPhone 18, and may switch to Linux/Kali if Apple remains problematic. Halfway through CompTIA+; need secure devices for VM, LLM/GPT isolation, Docker, and network segmentation (possibly with Pi-hole). Must be public here for due diligence; please recommend reputable firms or providers in comments. Thanks!
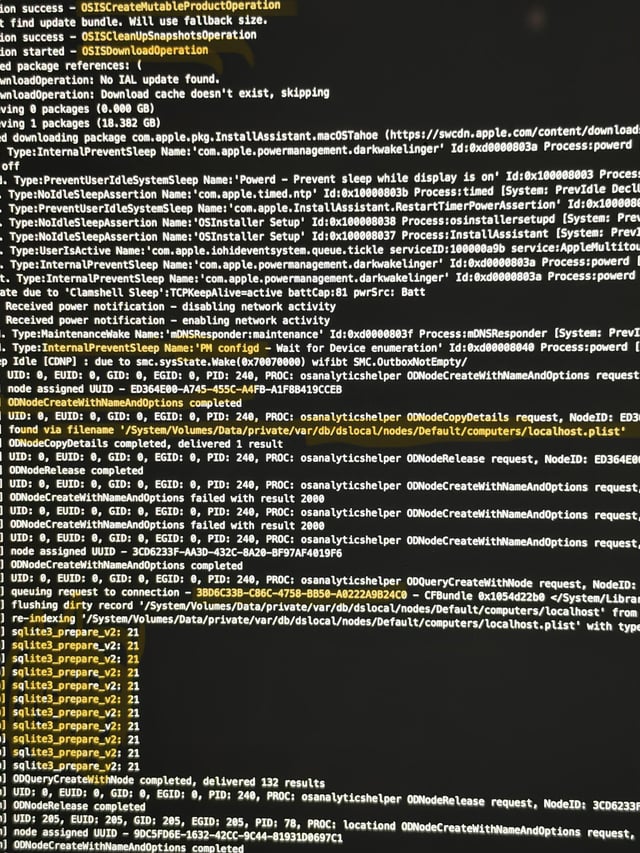
The bare minimum help I need: someone to help me determine for sure that my many attempts havent quashed the constant attack(s) / help at least detecting an existing attack vector, like,** ***for example, sensing/monitoring and access point that’s rogue somewhere in my house in helping me interpret the data I gather through like a USB adapter* w antenna or Wireshark or even what I’m going to attach here, which is the installer log errors only in the small section that didn’t look exactly right when I re-imagined my MacBook with a new copy of macOS Tahoe. However, it tells me I have to connect to a Wi-Fi network to do so, and I’d like to know if I I’m correct, and since I have nothing to hide and nothing besides data has been stolen at this point and nothing but my comfort and security has been violated, that I know of, (there are microtransactions consistently from Apple IDs, I cannot get into or cancel subscriptions from anymore, since they’re compromised & that probably adds up to a lot). I just have no one around me who even understands any of this technology whatsoever. My mom has to have help calling an Uber.** **
Ideally, comments that give me options or tell me how to deal with something like this, or where to go like to what consulting firm, etc, to handle it professionally, or** *do I just keep living life knowing that there’s nothing I can do and living in fear is no way to live at all.*
https://i.redd.it/0ruafsnmvyqh1.jpeg
Source: r/Cybersecurity101 · by /u/darekd124