For most of 2024 and 2025, "DPDP compliance" sat in the same mental folder as GST reconciliation, real but distant. That changed on 13 November 2025, when the Ministry of Electronics and Information Technology notified the Digital Personal Data Protection Rules, 2025, under Gazette Notification G.S.R. 846(E), giving full legal teeth to the Digital Personal Data Protection Act, 2023. The obligations now roll out in three phases through 13 May 2027, and Indian businesses of every size are quietly re-ranking their compliance priorities as a result.
What's notable isn't just that companies are paying attention. It's what they're switching to. A year ago, "DPDP readiness" usually meant a law firm engagement and a policy binder. In 2026, it increasingly means a subscription to a DPDP compliance automation platform — software that treats compliance as an operating process rather than a one-time document exercise.
The Deadline That Actually Concentrates Minds
Under the phased commencement schedule published by MeitY, the procedural provisions establishing the Data Protection Board of India took effect immediately on notification. Registration obligations for Consent Managers under Rule 4 become operational on 13 November 2026 — a little under two months from now. The heavier substantive obligations, including notice requirements, security safeguards, breach reporting, and the full suite of Data Principal rights, come into force on 13 May 2027.
That eighteen-month runway looks generous on a slide. It looks considerably less generous once a compliance team starts listing what actually has to happen inside it: a complete inventory of personal data across every business system, a rebuilt consent architecture, vendor contracts re-papered with DPDP-specific clauses, and a breach response process that's been tested, not just written.
None of that compresses well into a final quarter. Which is exactly why the shift toward automation is happening now, well ahead of the hard deadline, rather than closer to it.
What "Automation" Actually Means Here
It's worth being precise about what's changing, because "AI-powered compliance" gets used loosely. In the DPDP context, automation typically covers a specific, recurring set of operational tasks:
- Consent lifecycle tracking — logging when consent was given, for what purpose, and when it was withdrawn, automatically and with a timestamp, rather than reconstructed from memory when a Data Principal asks.
- Data Subject Request routing — assigning an owner, starting an SLA clock, and escalating automatically when a request for access, correction, or erasure comes in.
- Breach workflow triggers — under Rule 7 of the DPDP Rules, a Data Fiduciary must intimate the Data Protection Board and affected individuals without delay on becoming aware of a breach, then file a detailed report within 72 hours. Automation exists specifically to make that clock visible and impossible to miss.
- Vendor risk monitoring — recurring, scheduled reviews of every third party with data access, since accountability for personal data doesn't transfer away just because a vendor is the one processing it.
- Audit trail generation — every one of the above actions producing timestamped documentation automatically, so "show me the evidence" doesn't trigger a scramble.
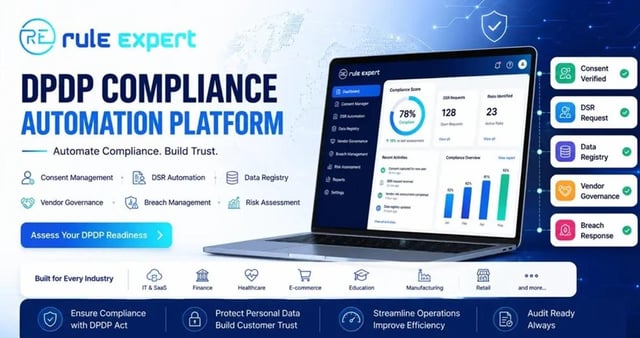
This is the category RuleExpert, an AI-powered DPDP compliance platform, has been built for. Rather than a single generic dashboard, the platform is structured around these exact operational surfaces: a DPDP Scorecard for initial readiness assessment, Consent Management, DSR Automation, a Data Registry, Breach Management, and Vendor Governance, all feeding one centralised, audit-ready documentation layer.
The Cost of Getting This Wrong Isn't Hypothetical
The Schedule to Section 33 of the DPDP Act sets some of the steepest monetary penalties of any data protection law globally, in absolute rather than turnover-linked terms. A failure to implement reasonable security safeguards that leads to a breach can draw a penalty of up to ₹250 crore. Failing to notify the Board and affected individuals about a breach carries a separate penalty of up to ₹200 crore. Violations involving children's data carry the same ₹200 crore ceiling, obligations specific to Significant Data Fiduciaries top out at ₹150 crore, and other violations can still reach ₹50 crore.
Because these figures are fixed rupee amounts rather than a percentage of revenue, the exposure lands disproportionately hard on smaller organisations — a reality the government itself acknowledged, having specifically consulted startups and MSMEs while finalising the Rules, according to the official MeitY/PIB backgrounder on the notification.
One detail worth flagging for anyone assuming the regulator itself isn't quite operational yet, so urgency can wait: the Data Protection Board of India was constituted in law from 13 November 2025 under Section 18 of the Act, and while legal press reported as of mid-2026 that its Chairperson and Members hadn't yet been formally appointed, the underlying statutory obligations, notice, safeguards, breach reporting, don't pause while the regulator's bench fills up. Courts have already begun treating the Board as an available remedy in early disputes.
Startups Aren't Exempt, Just Differently Exposed
A persistent misconception is that DPDP compliance is primarily an enterprise concern. It isn't. The Act applies regardless of company size; what changes with scale is the intensity of obligation. Organisations classified as Significant Data Fiduciaries under Section 10, based on qualitative factors like the volume and sensitivity of data processed rather than a fixed headcount, carry additional duties: Data Protection Impact Assessments, independent data audits, and a named accountability role under Rule 13.
For a lean team, the practical starting point isn't a full enterprise compliance build-out. It's a readiness assessment that turns a vague sense of exposure into a ranked list of what to fix first, which is precisely why platforms like RuleExpert lead with a scorecard-style diagnostic before anything else.
The Broader Pattern: From Policy to Infrastructure
What's happening in Indian DPDP compliance mirrors a pattern seen in other regulatory-heavy domains — anti-money-laundering compliance, cybersecurity frameworks, and international data protection regimes like GDPR all eventually moved from policy documents toward operational software, because policy alone can't produce evidence on demand. DPDP compliance automation is following the same trajectory, just compressed into a much shorter timeline than those other domains had.
For businesses still treating this as a legal exercise to be handled once and revisited before an audit, the practical risk isn't primarily legal anymore. It's operational: the gap between "we have a policy" and "we can prove compliance right now" is exactly where regulatory, reputational, and financial exposure concentrate. Platforms like RuleExpert exist to close that specific gap, turning DPDP obligations into infrastructure that runs continuously rather than a binder that gets dusted off once a year.
With roughly eight months remaining to the Consent Manager registration deadline and about twenty months to full enforcement, the organisations most likely to be caught out in 2027 aren't the ones who haven't read the Act. They're the ones who read it, agreed it mattered, and never got around to building anything.
Source: r/u/ruleexpertindia · by /u/ruleexpertindia